
Q1.At a manufacturing company, you are responsible for the security design of a Runbook placed in an Azure Automation account.
This Runbook periodically copies data to Azure Data Lake Storage Gen2.
You need to propose a solution to protect each component that makes up the copy process.
What should the recommendation for each component include?
To answer, select the appropriate option in the answer area.
Show answer
When the Runbook copies data to Azure Data Lake Storage Gen2, the access keys and secrets used for the connection should not be embedded in code, but stored and protected in Azure Key Vault.
For data security, store access keys in Azure Key Vault to reduce the risk of leaking sensitive information.
For network access control, it is important to configure communication to the Automation account and related resources so that it is not exposed to the public internet.
Azure Automation can be connected privately from a VNet by using Azure Private Link, and service tags simplify rule management.
For network access control, use Azure Private Link and network service tags.
The Automation Contributor role grants management permissions and the Web Application Firewall mainly protects web apps, so neither is suitable for this purpose.
Security best practices in Azure Automation
Use Azure Private Link to securely connect networks to Azure Automation
Network configuration for Azure Automation
Q2.A customer company uses Azure to develop a mobile app for external general consumers, configured as shown in the following exhibit.
You need to design the identity strategy for this app.
The solution must meet the following requirements.
Allow the use of external identities such as Google, Facebook, and Microsoft accounts.
Be managed separately from the customer’s identity store.
Support fully customizable branding for each app.
Which service should you recommend to complete the design?
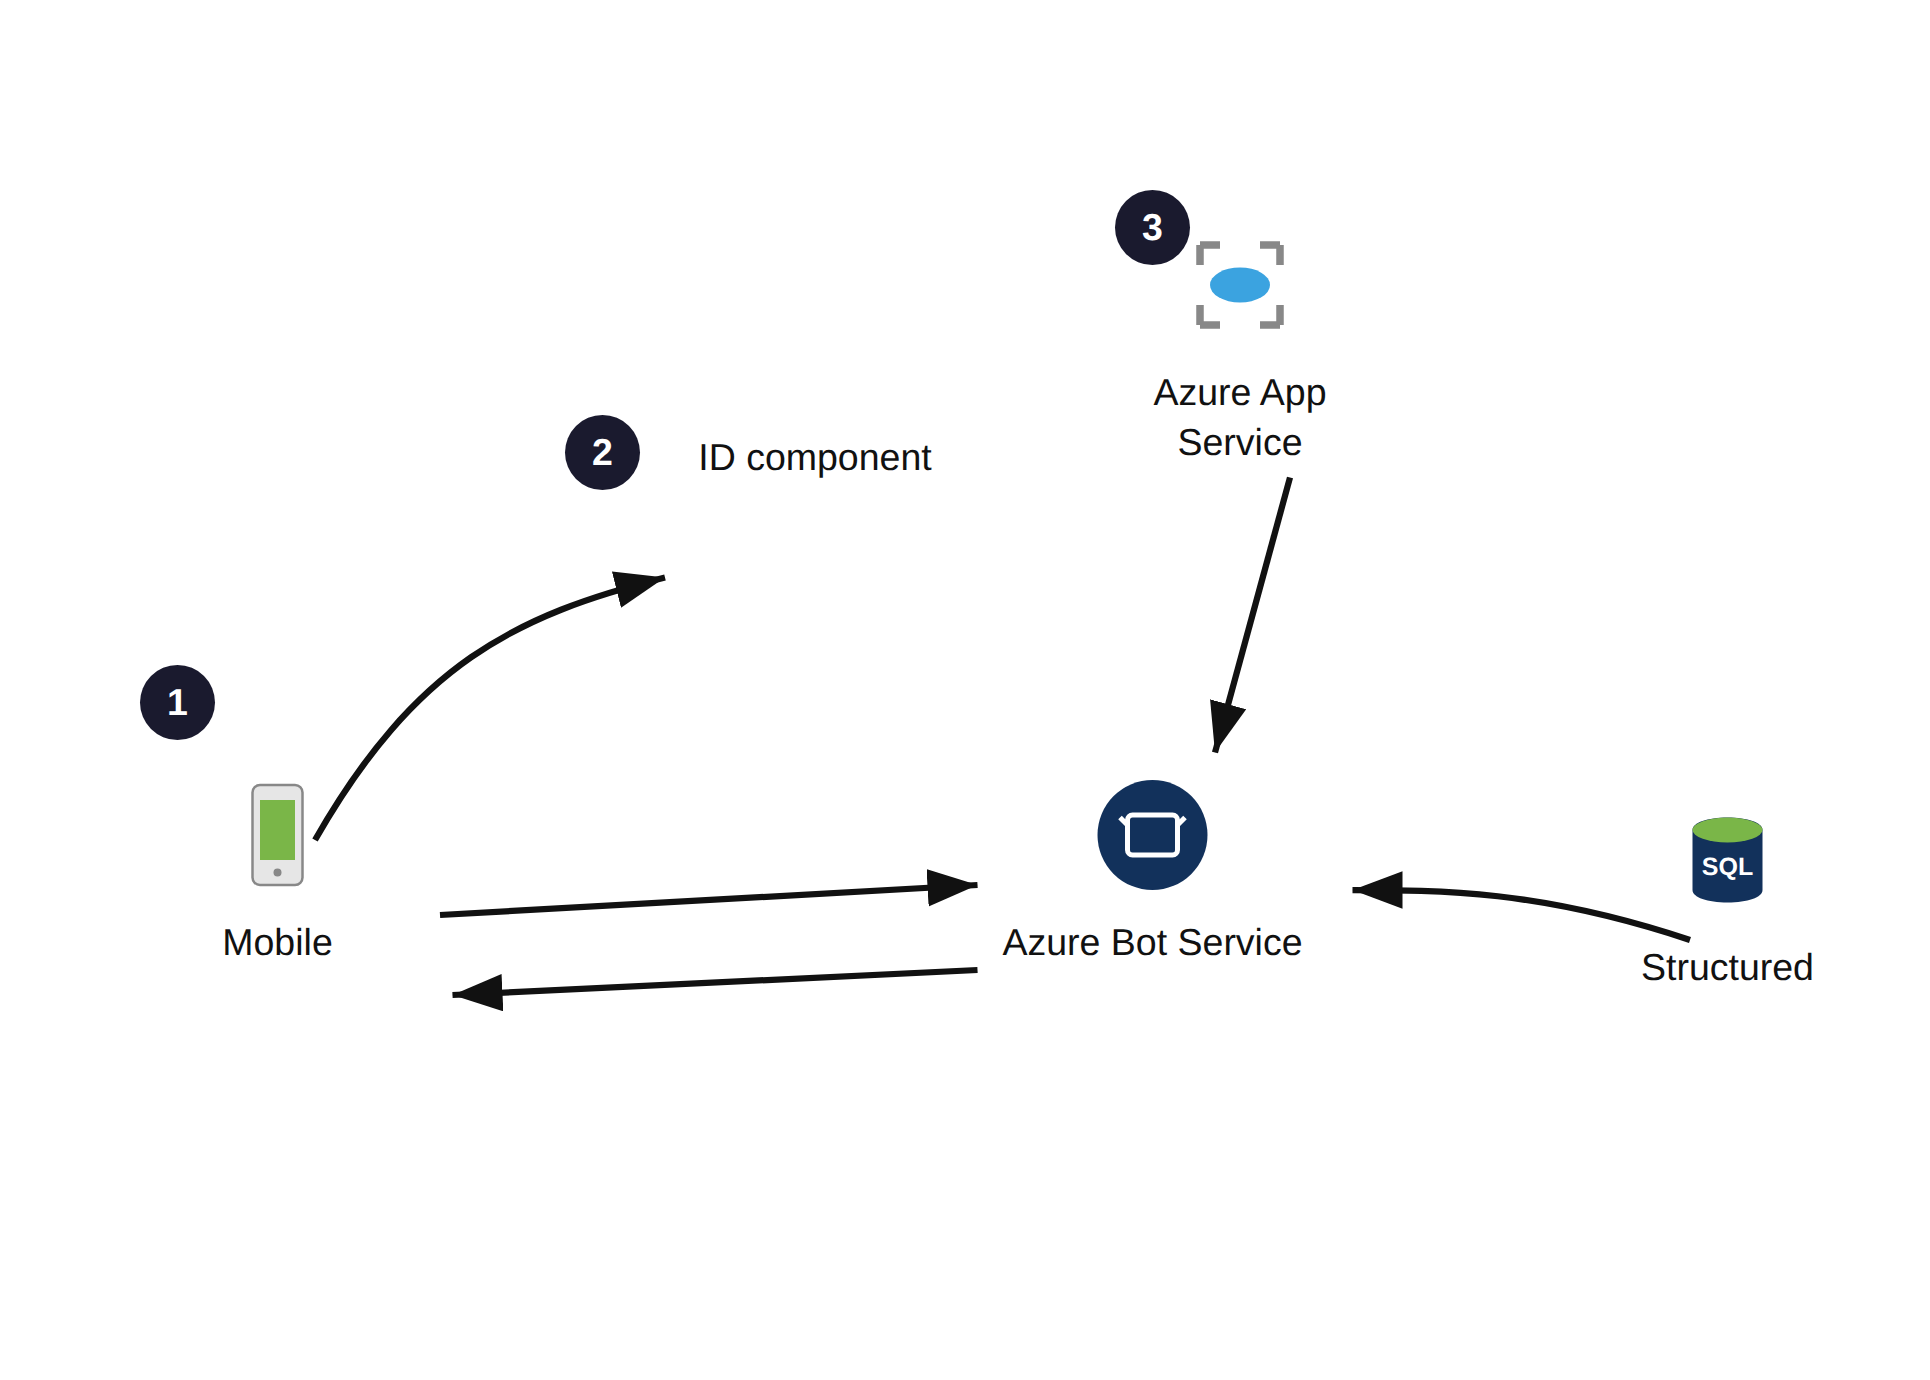
Show answer
The correct answer is A.
In the current Microsoft Entra framework, Azure AD B2C is positioned as the customer-facing identity capability of Microsoft Entra External ID.
It can authenticate external users with social identity providers such as Google, Facebook, and Microsoft accounts, and can be managed separately from the customer’s employee tenant.
In addition, the sign-up, sign-in, and password reset screens can be freely customized to match the app’s branding.
B2B is intended for sharing internal resources with partners and guests, so B2C is appropriate as an independent identity foundation for a consumer-facing mobile app.
Overview of Microsoft Entra External ID
Customize the UI by using HTML templates in Azure Active Directory B2C
Q3.You operate a Microsoft 365 subscription and an Azure subscription.
Microsoft 365 Defender and Microsoft Defender for Cloud are enabled.
The Azure subscription contains 50 virtual machines.
Each virtual machine runs a different application on Windows Server 2019.
You need to propose a solution that allows only approved applications to run on these virtual machines.
If an unapproved application attempts to run or install, it must be automatically blocked until an administrator approves it.
Which security control should you recommend?
Show answer
The correct answer is D.
Application control in Microsoft Defender for Endpoint uses Windows Defender Application Control (now App Control for Business).
You can implement an allow-list style control that permits only trusted applications to run.
Unapproved apps do not match the allow rules, so they are blocked from running until an administrator approves them.
Option A is session control when using cloud apps, Option B is monitoring of OAuth apps, and Option C is mainly data protection for mobile apps, so none of them are suitable for the requirement to control executable apps on Windows Server virtual machines by using an allow-list approach.
Note that Azure AD has been renamed to Microsoft Entra ID, and Endpoint Manager to Microsoft Intune.
Application Control for Windows
New name for Azure Active Directory
What is Microsoft Intune
Q4.You operate an on-premises datacenter that contains a server named Server1. Server1 runs Windows Server 2022.
There is also a firewall configured so that Server1 cannot connect to the internet.
You have an Azure subscription named Sub1.
You need to propose a resiliency strategy for Server1.
This strategy must include a backup plan that transfers data from Server1 to Sub1.
What should the recommendation include?
To answer, select the appropriate option in the answer area.
Show answer
Because Server1 is an on-premises Windows Server and not an Azure virtual machine, you install the Microsoft Azure Recovery Services (MARS) agent directly on the server and transfer files, folders, and system state to Azure Backup.
You specify a Recovery Services vault as the destination for the backup data, and the MARS agent registers the server by using the vault credentials.
The Azure VM extension is for virtual machines in Azure and cannot be applied to on-premises servers.
Because the firewall blocks the internet, note that you must allow the URLs required by Azure Backup or configure a private endpoint to ensure communication.
Tutorial: Back up Windows Server to Azure (MARS agent)
Support matrix for the MARS agent for Azure Backup
Q5.A company has a Microsoft 365 E5 subscription, an Azure subscription, on-premises applications, and Active Directory Domain Services (AD DS).
You need to propose an identity security strategy that meets the following requirements.
Allow customers to authenticate to an Azure App Service website by using their Facebook credentials.
Allow partner companies to access the Microsoft SharePoint Online sites for their assigned projects.
The solution must minimize the need to deploy additional infrastructure components.
What should the recommendation include?
To answer, select the appropriate option in the answer area.
Show answer
The correct answers are Azure AD B2C authentication for customers and Azure AD B2B authentication using access package assignment for partners.
Azure AD B2C is now a capability related to customer identity management in Microsoft Entra External ID, and it is suitable for sign-in to customer-facing apps that use social identity providers such as Facebook.
For partner companies, use B2B collaboration and assign access to resources such as SharePoint Online through access packages in entitlement management.
Both handle external identities while minimizing additional infrastructure, so they meet the requirements.
Note that Azure AD has been renamed to Microsoft Entra ID.
Overview of Microsoft Entra External ID
Add an identity provider to an Azure Active Directory B2C tenant
What is B2B collaboration in Microsoft Entra
Q6.You operate an Azure subscription.
This subscription contains 50 virtual machines running Windows Server and 50 virtual machines running Linux.
You need to perform a vulnerability assessment on these virtual machines.
The solution must meet the following requirements.
Identify missing updates and insecure configurations.
Use the Qualys engine.
What should you use?
Show answer
The correct answer is A.
Microsoft Defender for Servers is the server protection plan of Microsoft Defender for Cloud, and provides vulnerability assessment for Azure VMs, multicloud, and Azure Arc-enabled servers.
Under the premise of this question, the key point is that the built-in vulnerability assessment of Defender for Servers can use the Qualys engine.
Defender TI is for threat intelligence, Defender for Endpoint is for endpoint detection and response, and Defender EASM primarily manages the attack surface of externally exposed assets.
Note that integrated vulnerability scanning has now moved to Microsoft Defender Vulnerability Management, so in the latest environments you should also verify this change.
Overview of Microsoft Defender for Servers
Configure vulnerability scanning for machines
FAQ about machine vulnerability scanning using Microsoft Defender Vulnerability Management
Q7.Note: This question is part of a series of questions that present the same scenario.
Each question in this series contains a unique solution that might meet the stated goals.
Some question sets may have more than one correct solution, while others may have no correct solution.
After you answer a question in this section, you cannot return to it.
As a result, these questions will not appear on the review screen.
You have an Azure subscription with Microsoft Defender for Cloud enabled.
You are evaluating the Azure Security Benchmark V3 report.
You find that the Secure management ports control scored 0 out of a maximum of 8 points.
You need to propose a configuration to increase the score of the Secure management ports control.
Solution: You recommend enabling the VMAccess extension on all virtual machines.
Does this meet the goal?
Show answer
The correct answer is B.
To increase the Secure management ports score, you need a configuration that does not permanently expose management ports such as RDP and SSH to the internet.
Typically, you restrict access to management ports with Just-in-Time VM access or Adaptive Network Hardening.
The VMAccess extension is a feature used mainly to recover access to a virtual machine, manage users, and reset passwords or SSH configuration, and does not continuously control the exposure of management ports.
Therefore, simply enabling the VMAccess extension does not meet the requirement to improve Secure management ports.
NS-7: Simplify network security configuration
Just-in-Time machine access
VMAccess extension for Linux
Q8.You have an Azure AD tenant that is synchronized with an Active Directory Domain Services (AD DS) domain.
You are designing an Azure DevOps solution that deploys applications to an Azure subscription by using a continuous integration and continuous deployment (CI/CD) pipeline.
You need to propose the type of identity to use for the deployment credentials of the service connection.
The solution must follow the DevSecOps best practices of the Microsoft Cloud Adoption Framework for Azure.
What should you recommend?
Show answer
The correct answer is D.
For the credentials that an Azure DevOps service connection uses to deploy to an Azure subscription, a design that avoids long-lived passwords and user credentials is recommended.
An Azure managed identity lets you authenticate without storing secrets, because Azure automatically handles credential management and rotation.
A user account whose password is stored in Key Vault or a PIM-enabled user relies on human credentials, and a gMSA is mainly for on-premises Windows services.
In DevSecOps, using a non-interactive identity with least privilege is important.
Note that Azure AD has been renamed to Microsoft Entra ID.
Secure DevOps environments for Zero Trust
What are managed identities for Azure resources
Connect to Azure by using an Azure Resource Manager service connection
Q9.You have an Azure subscription with Microsoft Defender for Cloud enabled.
You are evaluating the Azure Security Benchmark V3 report.
You find that the Secure management ports control scored 0 out of a maximum of 8 points.
You need to propose a configuration to increase the score of the Secure management ports control.
Solution: You recommend onboarding all virtual machines to Microsoft Defender for Endpoint.
Does this meet the goal?
Show answer
The correct answer is B.
The Secure management ports control evaluates whether management ports such as RDP and SSH are not exposed to the internet or are properly restricted.
To increase the score, you need a configuration that restricts access to management ports with Just-in-Time VM access or Adaptive Network Hardening.
Onboarding to Microsoft Defender for Endpoint strengthens endpoint detection, response, and vulnerability management, but does not directly control the exposure state of management ports.
Therefore, simply onboarding to Defender for Endpoint does not meet the requirement to improve Secure management ports.
Secure score in Defender for Cloud
Just-in-Time machine access
NS-7: Simplify network security configuration
Q10.A company is migrating data to Azure, and that data contains personally identifiable information (PII).
The company plans to use Microsoft Information Protection for its PII data stores on Azure.
You need to propose a solution to detect risky PII data within Azure resources.
What should the recommendation include?
To answer, select the appropriate option in the answer area.
Show answer
The correct answers are Azure Purview and Microsoft Defender for Cloud.
Azure Purview is now offered as Microsoft Purview, and it can scan data sources such as Azure SQL Database and Azure Storage to detect and classify sensitive information such as PII.
Microsoft Information Protection is now also part of the Microsoft Purview Information Protection framework.
To prioritize, investigate, and triage the risks and alerts of Azure resources that contain detected sensitive data, use the security alerts and recommendations of Microsoft Defender for Cloud.
Protect sensitive data with Microsoft Purview
Security alerts and incidents